A wallet action fails. The balance did not move as expected. It is tempting to assume that every permission involved failed with it. With EIP-7702 delegation, that can be the wrong conclusion.
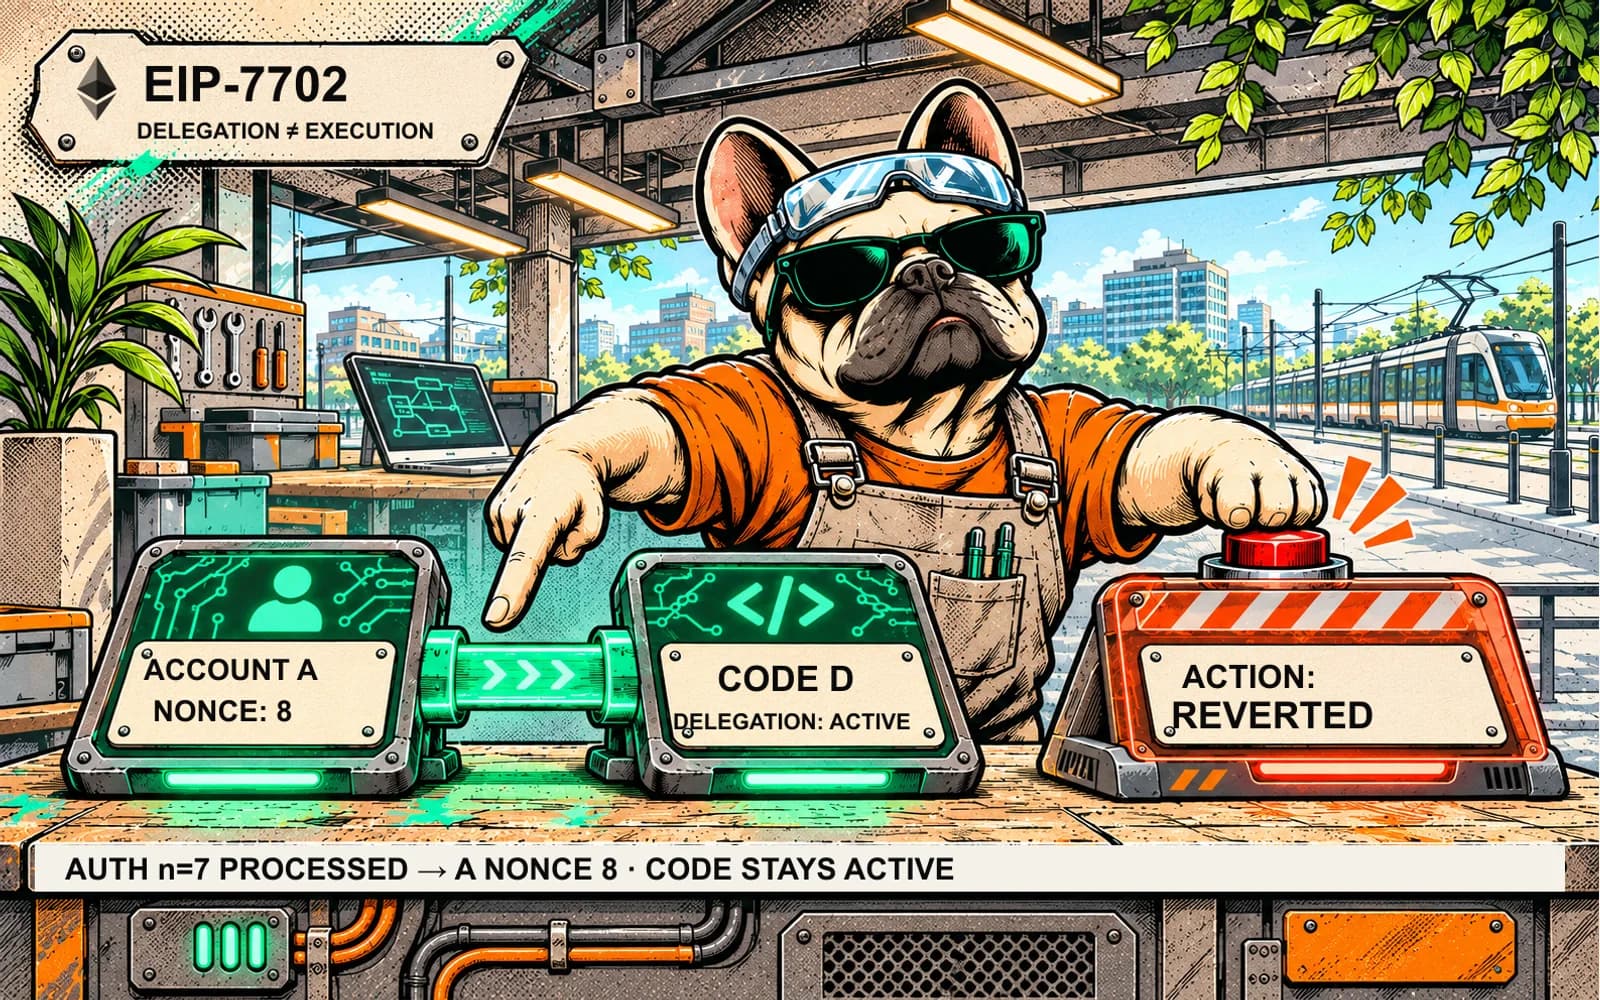
The mechanism has separate stages: signing an authorization, processing that authorization to set an account's code delegation, and executing an action. A signature alone does not complete the action. But a delegation already processed is not undone merely because the later execution reverts.
This explainer follows those stages through an invented account example. It describes the protocol, not a wallet interface or a procedure for signing, clearing or recovering a real account.
Where EIP-7702 is active
EIP-7702 reached Ethereum mainnet in Pectra on May 7, 2025, according to Ethereum.org's Pectra record. This is an explanation of an existing mechanism, not a new upgrade announcement.
That mainnet status does not establish support on every EVM chain, wallet or application. An integration still needs the actual network's rules and account implementation. Brokzi's smart-contract wallet overview covers the broader account choices; here the focus is the EIP-7702 authorization and its persistent effect.
An authorization points to code, not one token transfer
The current EIP-7702 specification introduces a type-0x04 transaction carrying an authorization list. Each authorization contains a chain ID, a delegate-code address, an account nonce and signature fields.
The authorization signature covers the chain ID, address and nonce in the specified signing format. The tuple is not a complete description of a swap, recipient, spending limit or deadline. Those restrictions cannot be assumed from the presence of an authorization signature.
When a valid tuple is processed, the protocol writes a delegation indicator into the authorizing account's code. Its form is 0xef0100 followed by the delegate address. Code-executing operations then load the pointed-to code and execute it in the authorizing account's context.
The delegate address identifies code. It is not simply the recipient of a token payment. That code can have broad account authority; its validation, execution and replay protections matter. The specification explicitly warns about poorly implemented delegates and requires account-action protections to be designed above this basic delegation mechanism.
Signing, installation and execution leave different evidence
Keep three questions apart:
- Was an authorization signed? A signature exists, but it has not necessarily been submitted or accepted.
- Was its tuple processed? The relevant account's code delegation and nonce may have changed.
- Did the intended action succeed? That requires evidence about the later execution and its actual effect.
The authorization list is processed before the transaction's execution portion, after the outer sender's nonce is incremented. Each tuple has its own checks, including chain context, signature, permitted existing code and the authorizing account's current nonce.
A tuple failing a processing check is skipped; processing continues with the next tuple. Multiple valid tuples for the same authority can appear, with the last valid one determining its delegation. Inclusion of the outer transaction alone therefore does not prove that one selected authorization took effect.
One fictional account: nonce 7, then 8, then 9
Suppose fictional account A initially has empty code and nonce 7. Its owner signs an authorization pointing to invented delegate D, representing ordinary deployed delegate code, using A's nonce 7 and the chosen chain ID. A separate fictional sender S submits the enclosing transaction and pays its network gas.
Assume all validity checks pass for the specified tuples. A sends no ordinary transactions during the example, no other authorizations are processed for A, and delegated execution creates no additional nonce changes. These exclusions keep the counters readable; they are not assumptions you can make about a live account.
| Observation | A's nonce | A's code |
|---|---|---|
| Initial state | 7 | Empty |
| Authorization to D is signed only | 7 | Still empty |
| Valid authorization is processed; later execution reverts | 8 | Delegation indicator pointing to D remains |
| A clearing authorization using nonce 8 is signed only | 8 | Still delegated to D |
| That valid clearing authorization is processed | 9 | Empty code |
The counter arithmetic is 7 + 1 = 8, then 8 + 1 = 9: one increment for each successfully processed authorization in this example. Merely signing either authorization changes neither field.
The row containing a revert is the important one. The EIP explicitly says processed delegation indicators are not rolled back by subsequent execution failure. The intended call can fail while A remains delegated to D. A “failed” action is not a substitute for checking A's resulting code state.
No account, signature, sender, code installation, clearing request or transaction in this table exists on a network. This is a state-transition example, not captured RPC output or a signing recipe.
The authorization nonce is not an expiry timer
The tuple's nonce must match the authorizing account's nonce when processed. After the first valid authorization in our example, A's nonce is 8. The earlier tuple carrying 7 no longer satisfies that check. That does not remove the delegation already installed at D.
Nor does EIP-7702 add a universal time-based expiry to the authorization tuple. A pending signature must be evaluated against the actual chain and nonce conditions; a delegation already installed persists until changed or cleared through valid processing. Account-code logic may impose its own limits, but that is a different layer.
The example uses a separate sender S deliberately. If the transaction sender also authorizes its own delegation, the outer sender's nonce has already been incremented before authorization processing. Treating those two moments as one unchanged counter produces a bad example. Brokzi's Ethereum nonce guide explains the underlying account sequence and why it is not a count of successful payments.
Clearing code is a processed change, not an undo button
The EIP gives a special meaning to an authorization whose delegate address is the zero address: on valid processing, the account's code is cleared instead of storing a delegation indicator. The authorizing account's nonce is still incremented.
Signing such an authorization is not enough. It needs to be valid and processed in the relevant state. A different valid authorization or other nonce-changing activity can affect whether a previously signed clearing tuple remains usable. This article does not prescribe a cancellation transaction or promise which competing request wins.
Clearing code also does not reverse earlier transfers or reset the account's history. Changing delegates is not a storage-cleaning operation: the specification separately discusses storage collisions when different implementations interpret existing account storage. Do not read “delegation cleared” as a complete account or permissions audit.
The underlying key also remains significant. Delegated EOAs can still originate transactions under the protocol's applicable rules. Adding delegated logic does not establish that the original key has lost its authority.
A chain ID of zero does not update every chain at once
Authorization processing accepts a tuple chain ID of zero or the current chain's ID. A zero value permits cross-chain use subject to each chain's support and state checks. It does not broadcast a transaction or install code on every chain by itself.
The same delegate address can also require separate code verification on another network. Keep chain, account, delegate address and observed state together. No list of universally supported networks or approved delegate contracts is supplied here.
What a useful status explanation should show
For an EIP-7702-related action, distinguish the signed authorization from its processing result, the account's resulting delegation, and the intended action's outcome. Include the relevant chain, authority, delegate and nonce context rather than relying on a generic “approved” badge.
ERC-4337 UserOperations provide an operation-processing route that can interact with EIP-7702. ERC-1271 answers a contract-signature validation question. Neither replaces the delegation-state checks described here.
The practical reading rule is specific: a signed authorization is not a completed action, and a failed action does not prove that a processed delegation disappeared. Establish which stage the evidence actually describes before interpreting the result.
Sources
The complete current EIP-7702 specification and Ethereum.org's Pectra record were checked November 4, 2026. The mainnet activation date remains May 7, 2025; no new event is claimed. Protocol support does not establish wallet, application or other-chain availability.
A, D, S and the 7-to-9 sequence are invented. Counter transitions were checked locally against the stated assumptions. No wallet connection, signature creation, RPC request, code deployment, account delegation, clearing transaction, token transfer, recovery action or security audit was performed. The artwork is a fictional mechanism illustration, not a live account record.
- EIP-7702: Set Code for EOAs: authorization fields and processing, persistent delegation, execution failure, nonce, chain scope, clearing and security boundaries.
- Ethereum.org: Pectra: Ethereum mainnet activation and inclusion of EIP-7702.
See something wrong? Brokzi logs material changes. Prepare a correction note.