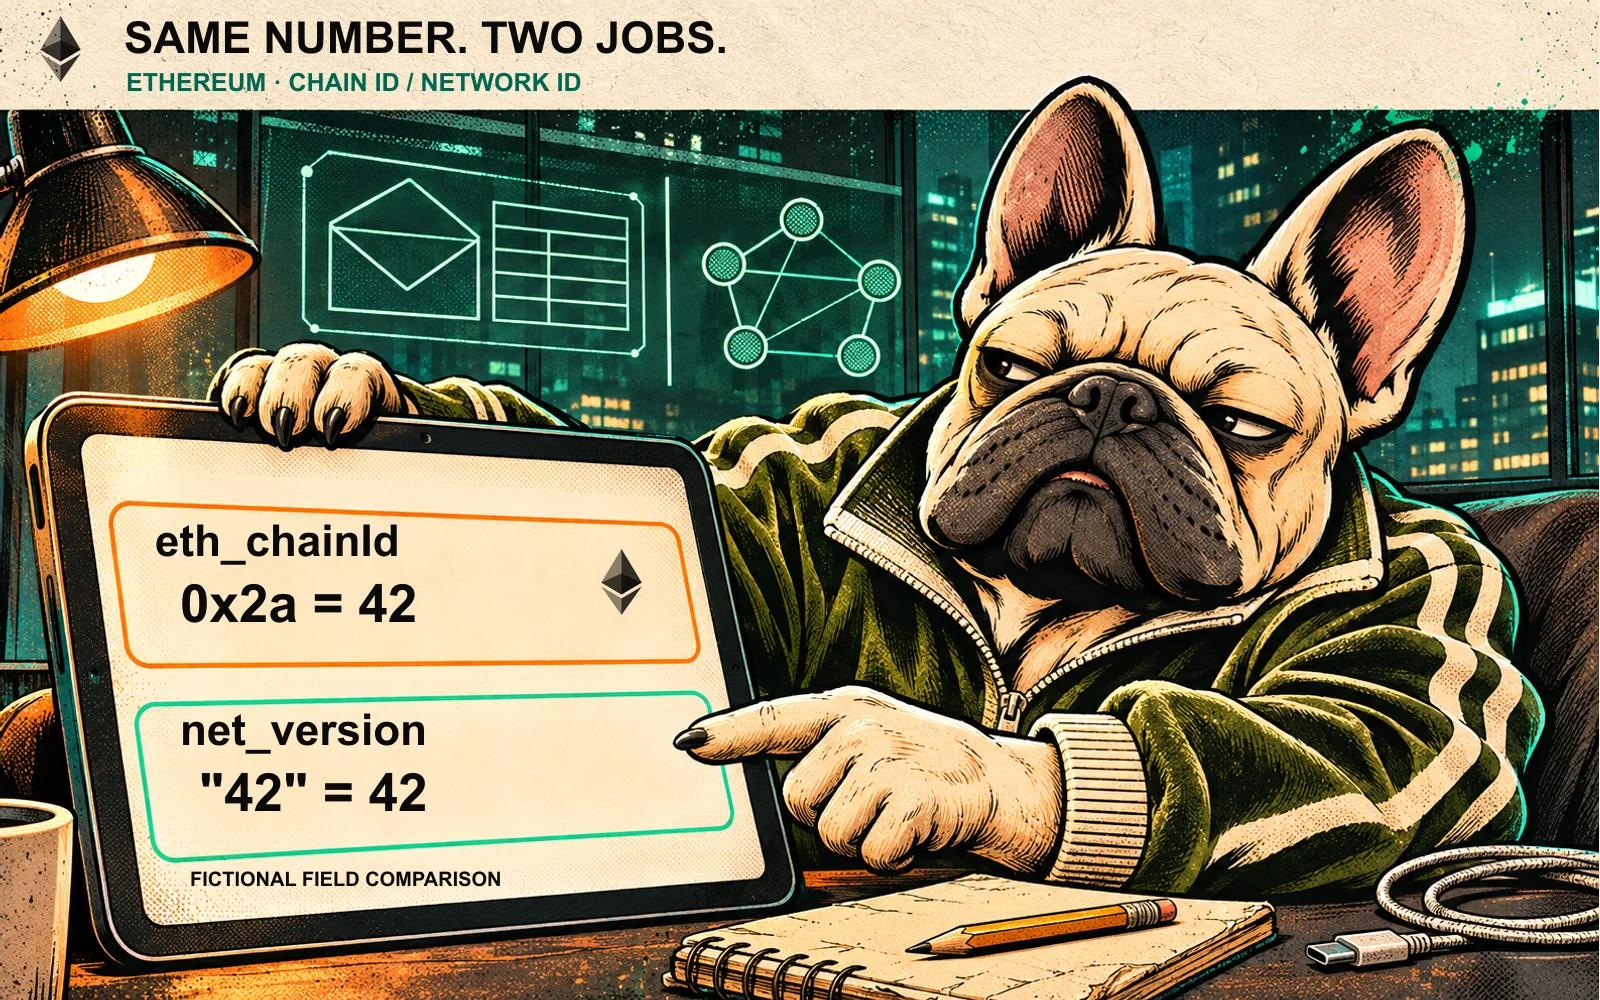
Two Ethereum-related fields can both show the number 1 and still describe different things. One identifies a signing context. The other identifies a networking context. Reading the number without its field name loses that distinction.
Ethereum's chain ID is used in transaction signing and validation rules. In Geth, net_version reports the devp2p network ID. The values often agree, but the fields have different jobs and can differ. Neither number authenticates a token, project or RPC endpoint.
This explainer is for readers comparing wallet details, documentation or a saved node response. It uses fictional field values, without connecting to a node or preparing a transaction.
Chain ID vs network ID: compare the field first
Keep these three records separate:
| Record | What it identifies | How to read it |
|---|---|---|
| Chain ID in a transaction's signing context | The chain context required by that transaction format | Follow the format's signing and validation rules |
eth_chainId response | The execution client's reported chain ID | A hexadecimal quantity string in the checked API contract |
Geth net_version response | The client's devp2p network ID | A decimal integer string in the checked API contract |
The Geth net namespace documentation, edited on 9 November 2026, explicitly calls net_version a devp2p network ID. This concerns the client's networking layer.
The Execution API client specification defines both methods. It says the network ID is usually equivalent to the chain ID, while allowing differences on legacy networks or special testnets. Agreement is common; interchangeability is not the rule.
The net_version method name does not make its result a software version. A number in that field is not a Geth release number or the version of an application's smart contract.
What EIP-155 puts in the signing context
EIP-155 introduced its replay-protected legacy transaction signing scheme with Spurious Dragon. In that scheme, the signing hash incorporates the chain ID alongside the transaction's other signing fields.
Specifically, the protected route extends the six legacy signing elements with the chain ID and two zero values, making nine elements. Its signature recovery value also encodes the chain context under the EIP's rules. A devp2p network ID returned by net_version is not an extra field in this construction.
That is a statement about this particular signing format. It is not a universal serialization recipe for every Ethereum-related request. Typed transactions have their specified formats. EIP-712 typed messages, smart-account operations and account-delegation authorizations also need their own rules.
The distinction matters when a screen simply says “sign.” First identify the request type. A chain ID shown somewhere in the interface does not establish which fields the actual request encodes or what accepting it can do.
Hexadecimal and decimal can describe the same number
The checked Execution API base types define uint as a hexadecimal quantity string and uintDecimal as a decimal unsigned-integer string. The client module uses the former for eth_chainId and the latter for net_version.
For example, hexadecimal 0x2a is decimal 42: 2 × 16 + 10 = 42. Comparing the two printed strings character by character would miss that equality.
Here are three deliberately invented records. They name no real chain or service and are not captured RPC responses:
| Fictional record | eth_chainId | net_version |
|---|---|---|
| A | 0x2a → 42 | "42" → 42 |
| B | 0x2a → 42 | "77" → 77 |
| C | 0x2b → 43 | "42" → 42 |
In A, the numbers agree after decoding, but still occupy different fields. In B, the same reported chain ID accompanies a different network ID. In C, the network ID matches A's while the reported chain ID differs.
These rows illustrate the separation permitted by the documented concepts. They do not predict whether any pair of real nodes would connect, share a genesis block, accept a transaction or observe the same chain history. No node was configured or queried.
When checking a saved record, retain the method name, encoding, source and observation time. A bare “42” in a screenshot leaves too much context behind.
Why a chain ID does not stop every replay
EIP-155 adds chain context to its protected legacy signing input. Different encoded chain IDs separate that context under the specified scheme. This is useful protection, with a defined boundary.
The ID is a number, not a guarantee that no other chain uses it. Two environments using the same chain ID do not gain separation from that number alone. Other transaction conditions still matter; the number is not a universal verdict on whether a particular transaction could be accepted elsewhere.
EIP-155 also retains the earlier signature scheme in its specification. That does not promise that a current provider accepts every unprotected transaction or automatically applies replay protection to every request. Provider policy, transaction format and application-message rules are separate questions.
For typed messages, EIP-712 explicitly leaves replay handling to applications. A nonce or deadline helps only under rules that define and enforce it. Our Ethereum nonce explainer separates the account's transaction counter from a token permit's counter; those should not be folded into a generic “network protection” badge.
Matching IDs do not authenticate the project
Suppose a website displays the chain ID you expected. That observation does not establish who operates its RPC endpoint, which history it serves, who controls a contract or whether a receiving service supports a deposit.
An ID is part of the context you need to establish. It is not an identity certificate supplied by the protocol. A malicious or misconfigured service can display reassuring labels; a reported number alone cannot resolve that trust question.
For tokens, keep the actual network and full contract address together, as our token identity guide explains. A familiar ticker and a familiar chain ID do not establish that the issuer deployed that contract. The destination's supported route is another independent check.
Likewise, a correctly identified signing context can still contain an unwanted destination, value or action. The connection, signature and approval comparison covers those permission layers. This article does not recommend signing a request merely because one number matches.
A read-only checklist for the two identifiers
- Name the record. Is it a transaction field, an
eth_chainIdresponse, a Gethnet_versionresponse or an application's own label? - Read the encoding. Convert a documented hexadecimal quantity before comparing it with a decimal string. Keep the field names attached even when the values agree.
- Establish the source. Record which documentation, client or provider supplied the information and when. A method name does not verify the endpoint's identity.
- Check the request's format. Identify the signing scheme and complete action separately. Do not import EIP-155's legacy serialization into every typed message or authorization.
- Keep identity and outcome separate. Establish the intended chain, contract and receiving route independently. An ID match does not prove execution, payment or deposit credit.
Chain ID and network ID become useful when you keep their roles visible. Compare decoded values, then return to the question each field can actually answer.
Sources and scope
Primary sources checked on 21 November 2026. EIP-155 is a Final Core specification created on 14 October 2016. Its historical Spurious Dragon fork block and old network-ID table are not a new announcement or a current directory of networks.
Geth's net page identifies its last edit as 9 November 2026. That is a documentation date, not the version of a running Geth binary. The Ethereum.org JSON-RPC reference is a rolling document with older examples and tutorials; no node setup, key, signing or deployment example was executed.
The complete Execution API client module and base-types schema were captured as verified Git blobs 2158b187a2c229ebb590191680d95447d292de3f and d5276a24755689ab605d67d7144deb6c97c49baa. These identify file contents, not a repository commit, release or a tested client implementation. The linked branch pages may change after this check.
The table and conversion are fictional teaching material. No live network mapping, wallet, address, secret, RPC request, signature, transaction or replay test was used. This is an explanation of documented fields, not signing instructions, a client audit or financial advice.
- EIP-155: Simple replay attack protection — the protected legacy signing context and its historical scope.
- Geth: net namespace —
net_versionas devp2p network ID. - Execution API: client methods — separate
eth_chainIdandnet_versioncontracts. - Execution API: base types — hexadecimal and decimal unsigned-integer strings.
- Ethereum.org: JSON-RPC API — method contracts and quantity conventions, with the scope limits above.
See something wrong? Brokzi logs material changes. Prepare a correction note.